Ransomware behavior detection
Monitors canary file changes, unusual file entropy and rename patterns that may indicate ransomware activity.
Defendria
Sentinel is Defendria’s endpoint detection and response (EDR) platform for IT teams in small and midsize organizations. Monitor endpoints, investigate alerts and manage response in one console.
Information for your security review
Detection and protection
Review process, file and network activity from enrolled endpoints. Sentinel combines detection layers with the evidence needed to investigate a finding.
How detection fits the workflowMonitors canary file changes, unusual file entropy and rename patterns that may indicate ransomware activity.
Examines document text and page images for phishing cues. The resulting verdict and analysis context can be reviewed with the file evidence.
Looks for suspicious PowerShell activity, abuse of Windows utilities, AMSI bypass indicators and reflective loading patterns.
An investigation in practice
Follow the parent process, associated file and outbound connection to understand what led to the alert.
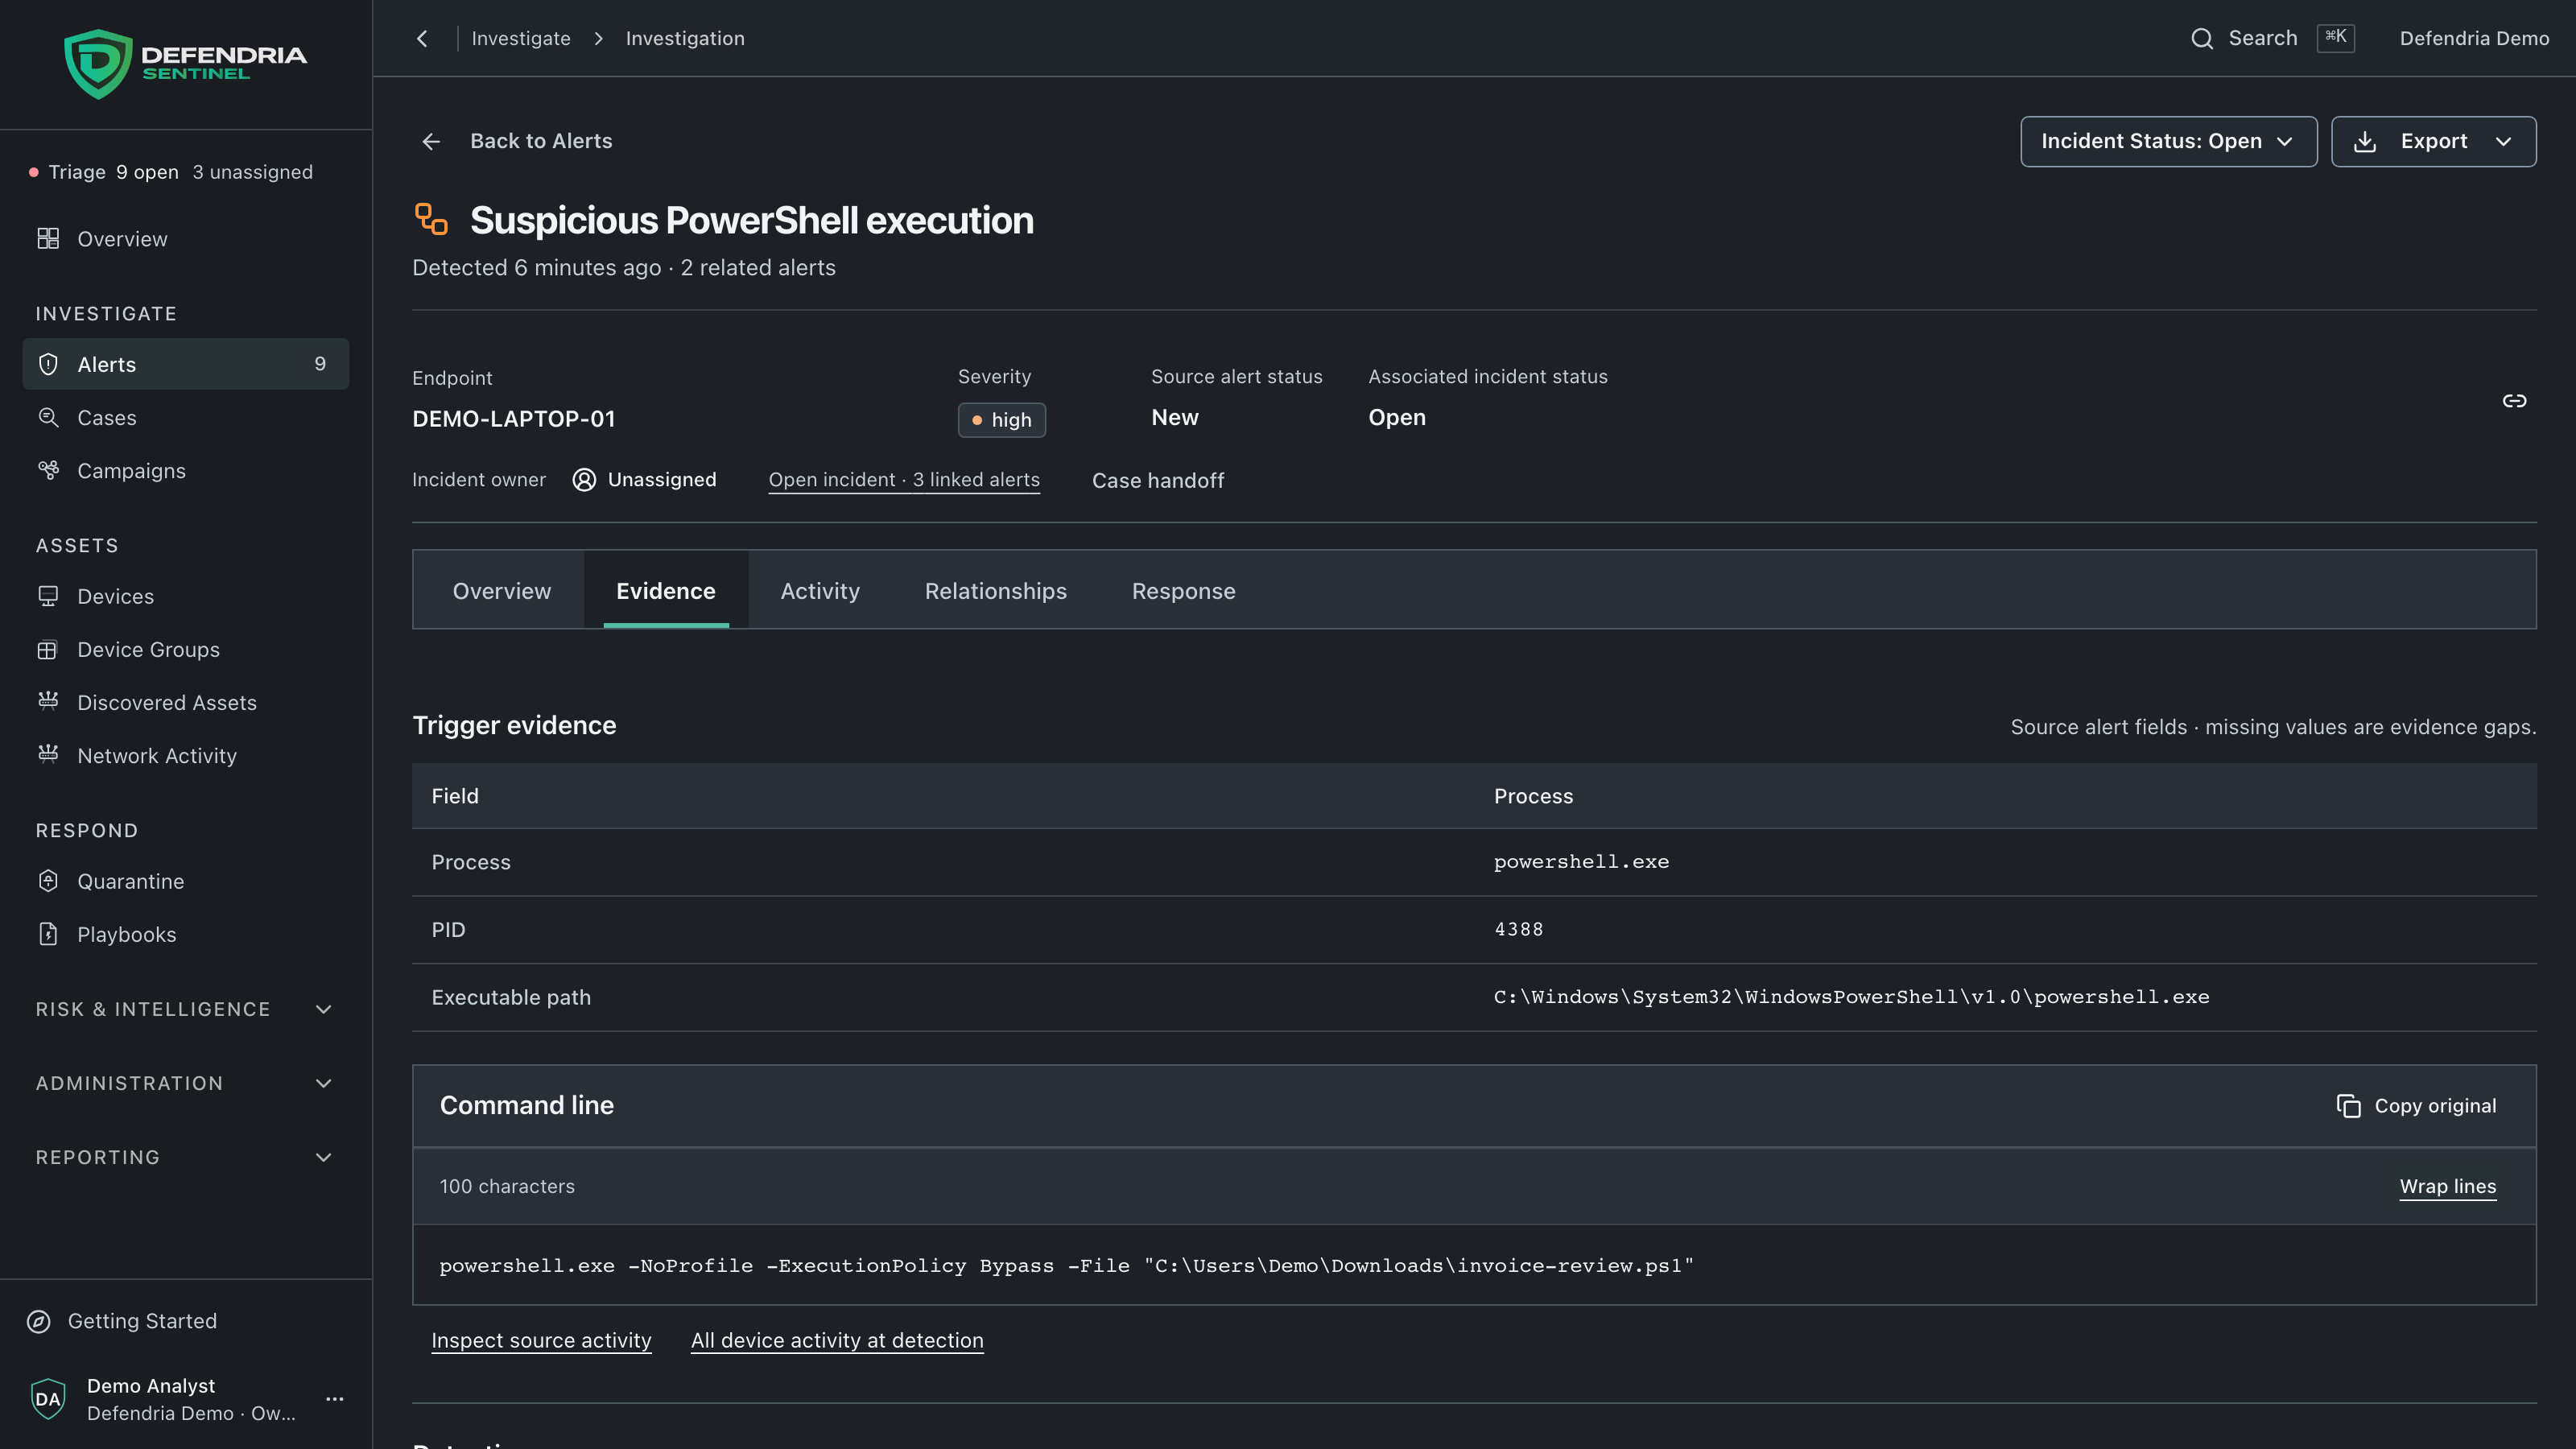
See the investigation viewSee the screens your team uses to review alerts, manage devices and follow up on actions.
Product detailsInspect the source process and command line, follow the activity timeline, and review related entities.
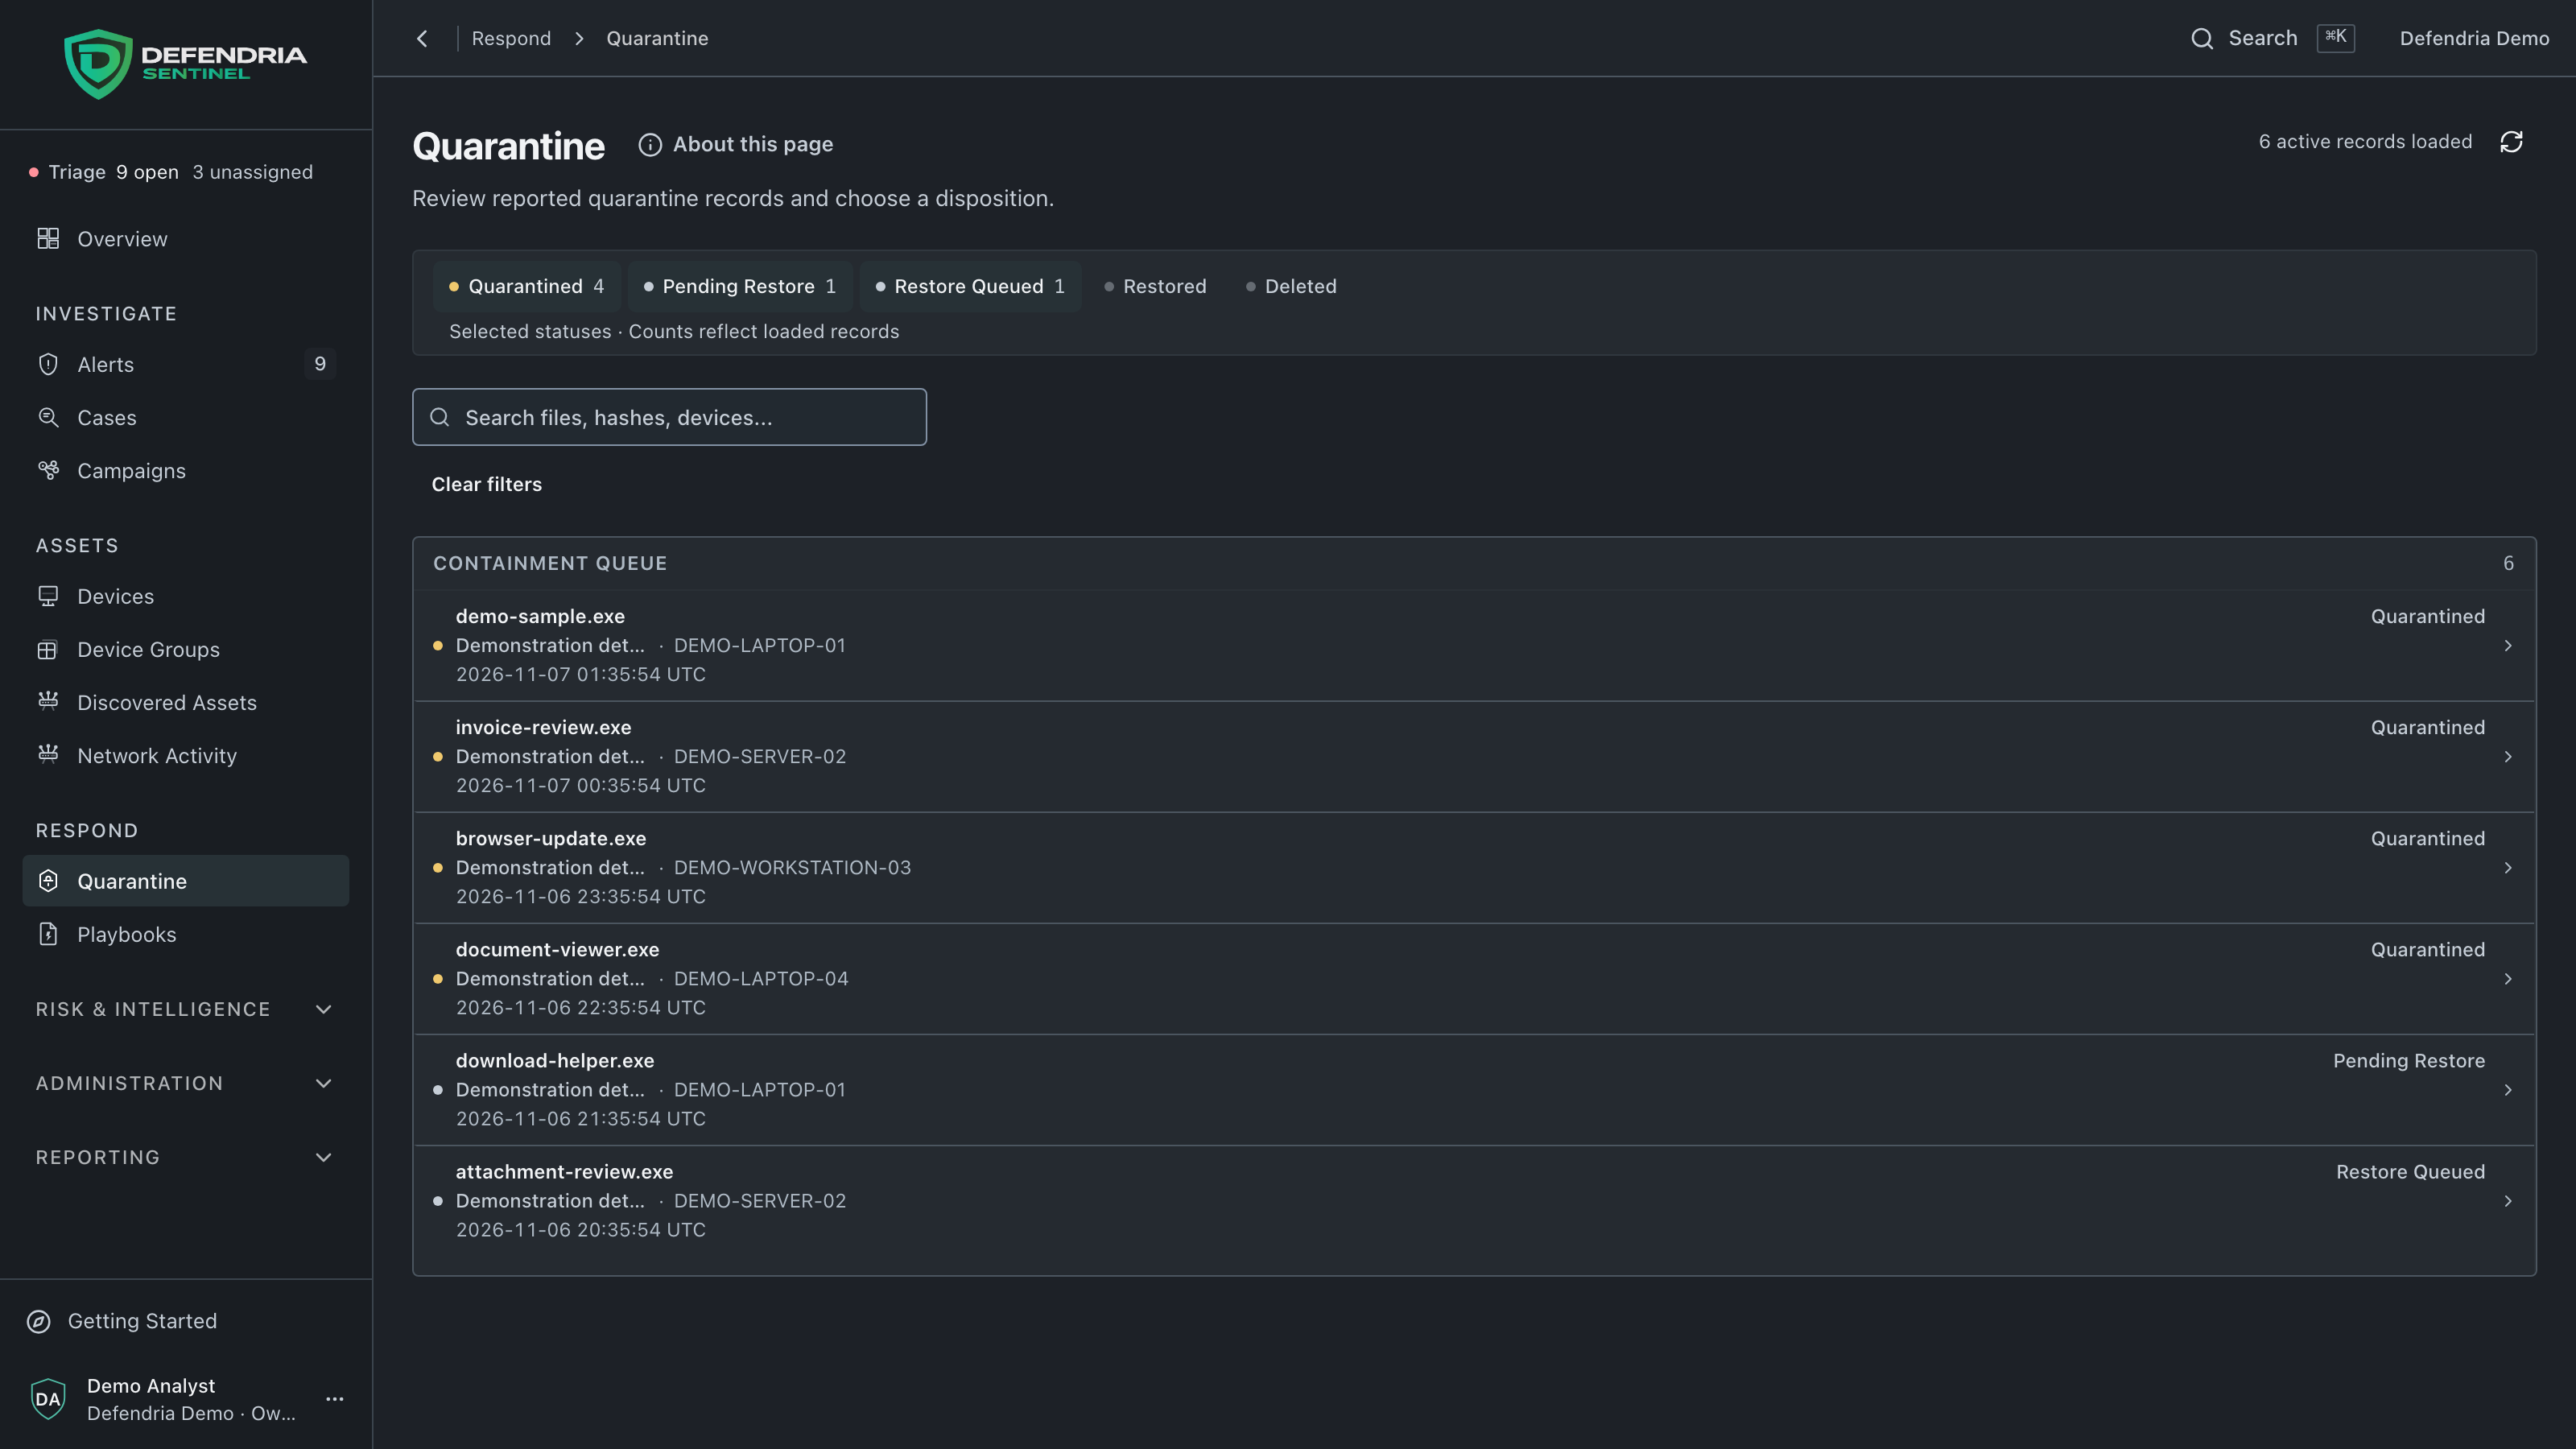
Available controls depend on permissions, policy and device state. Check the reported result after requesting an action.
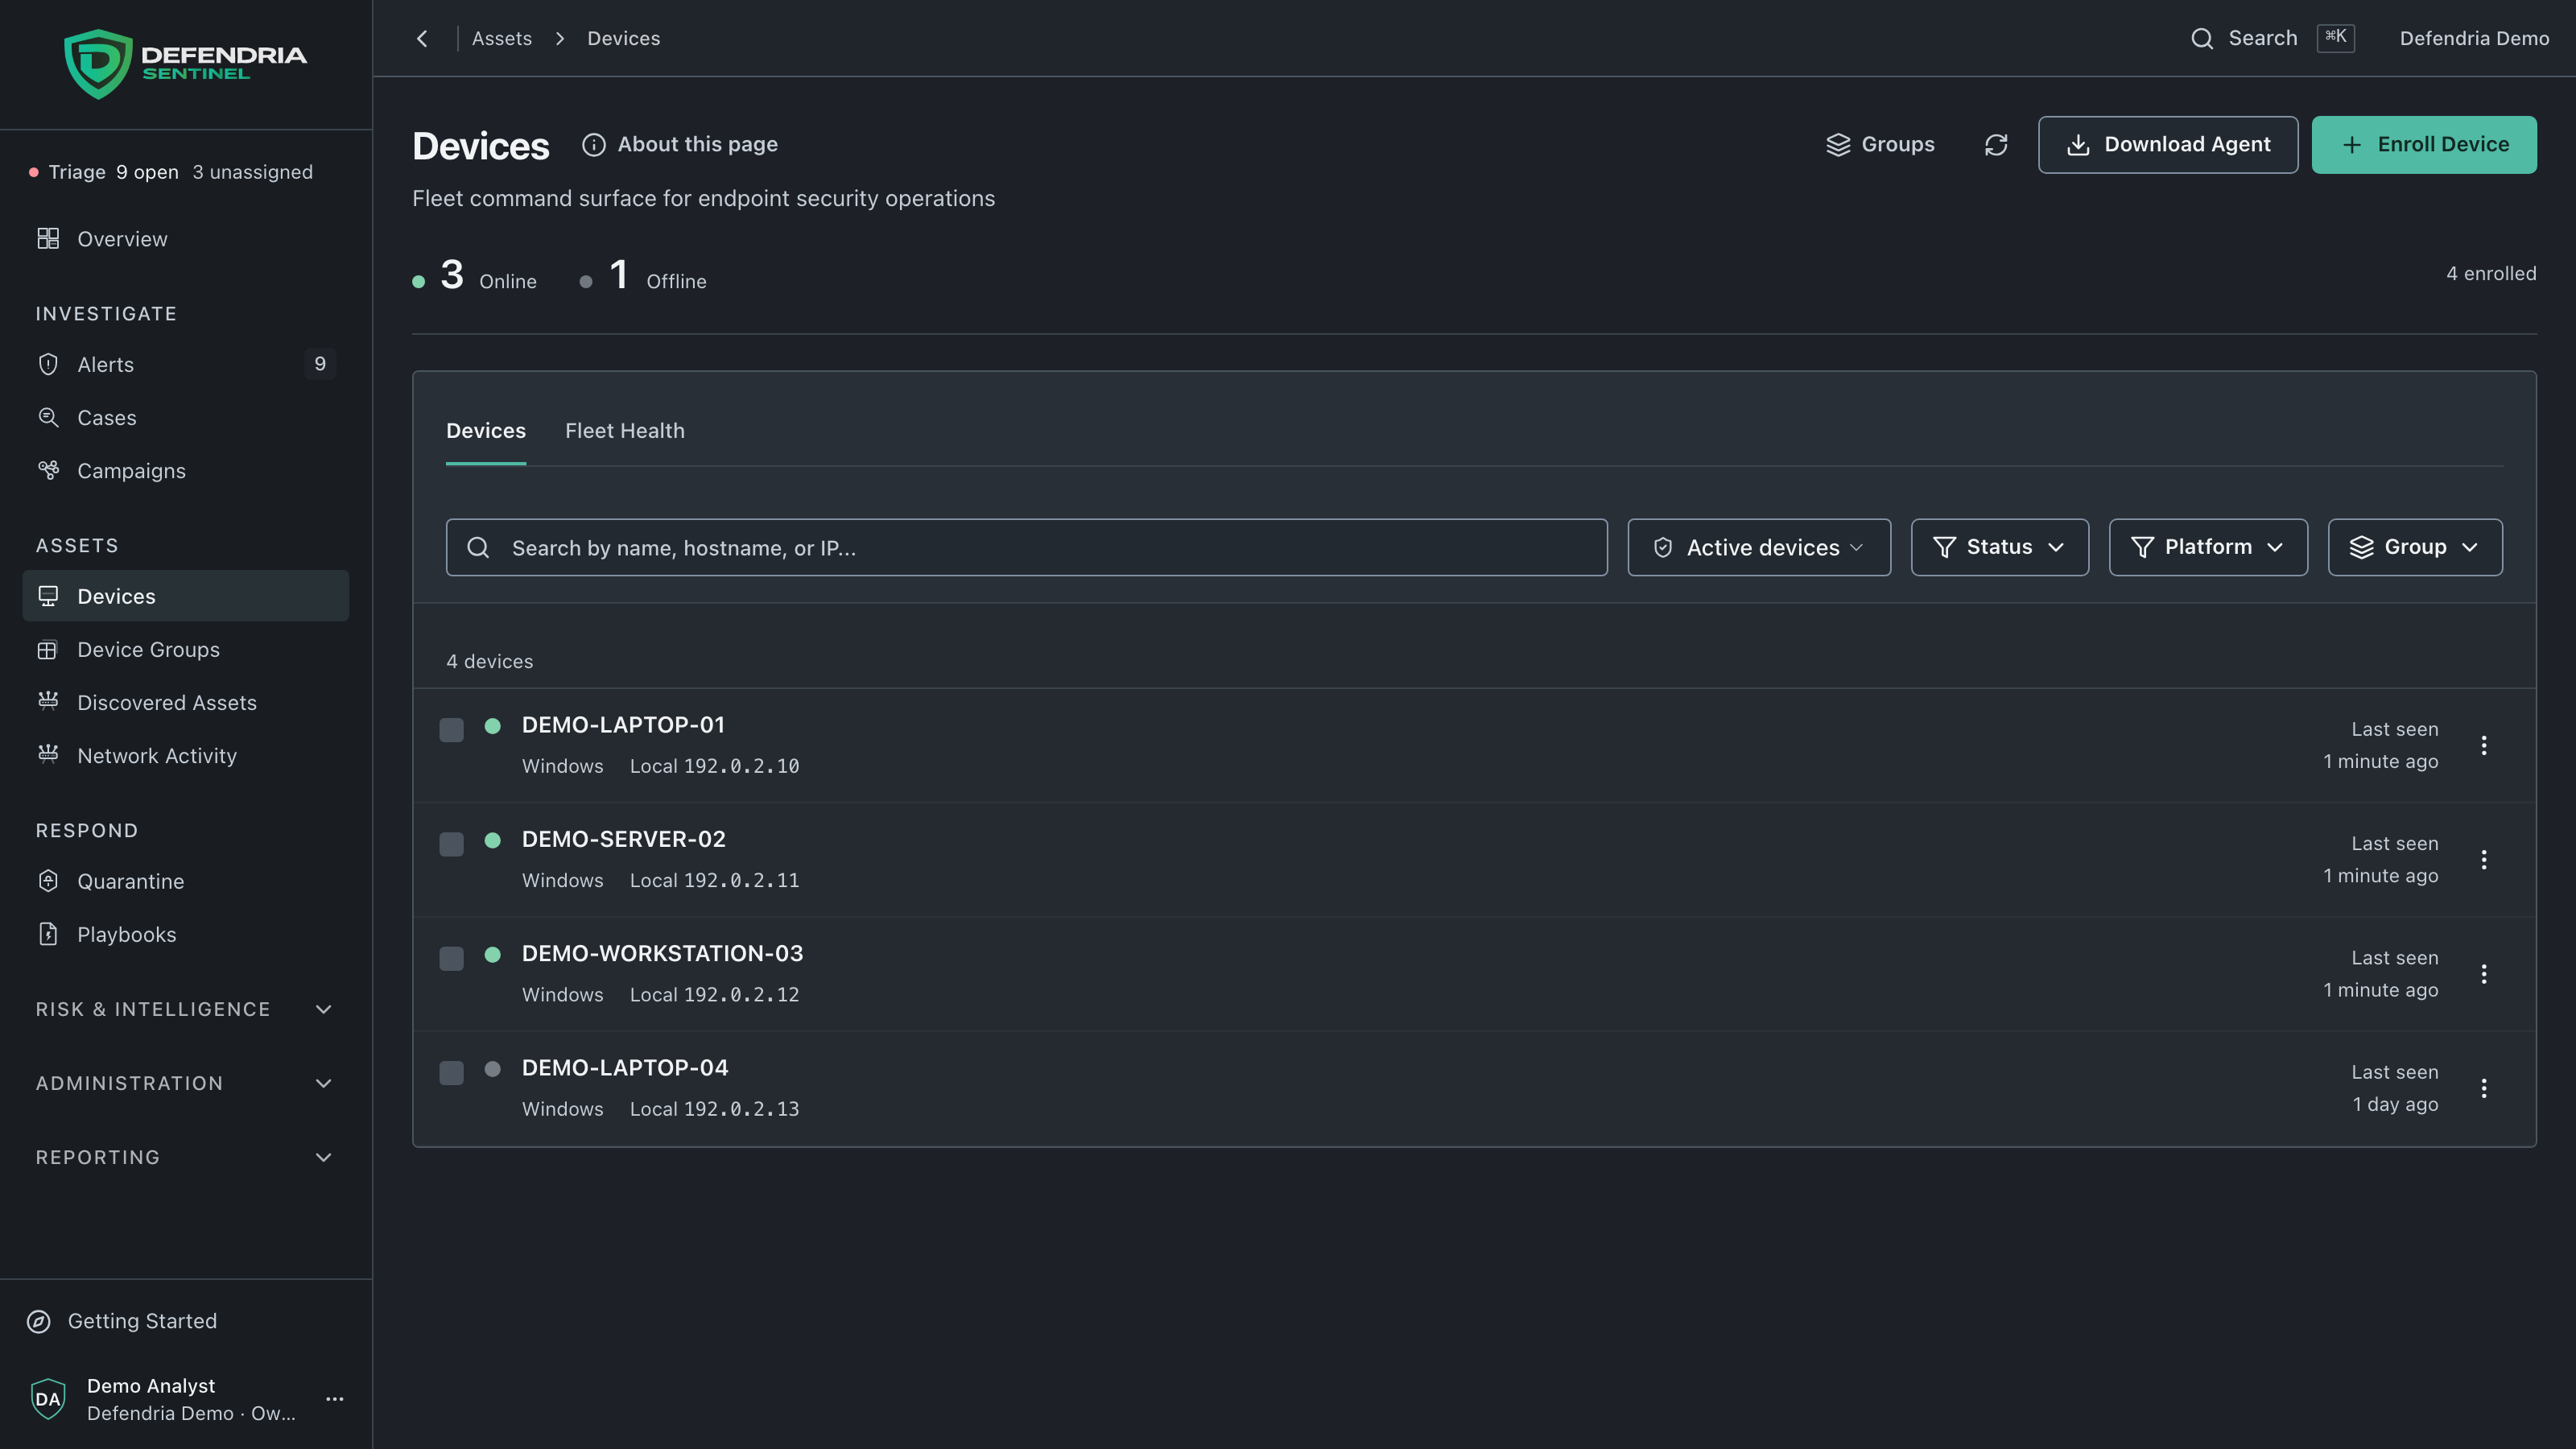
Check last-seen times and reporting gaps. Group devices to manage policy assignments.
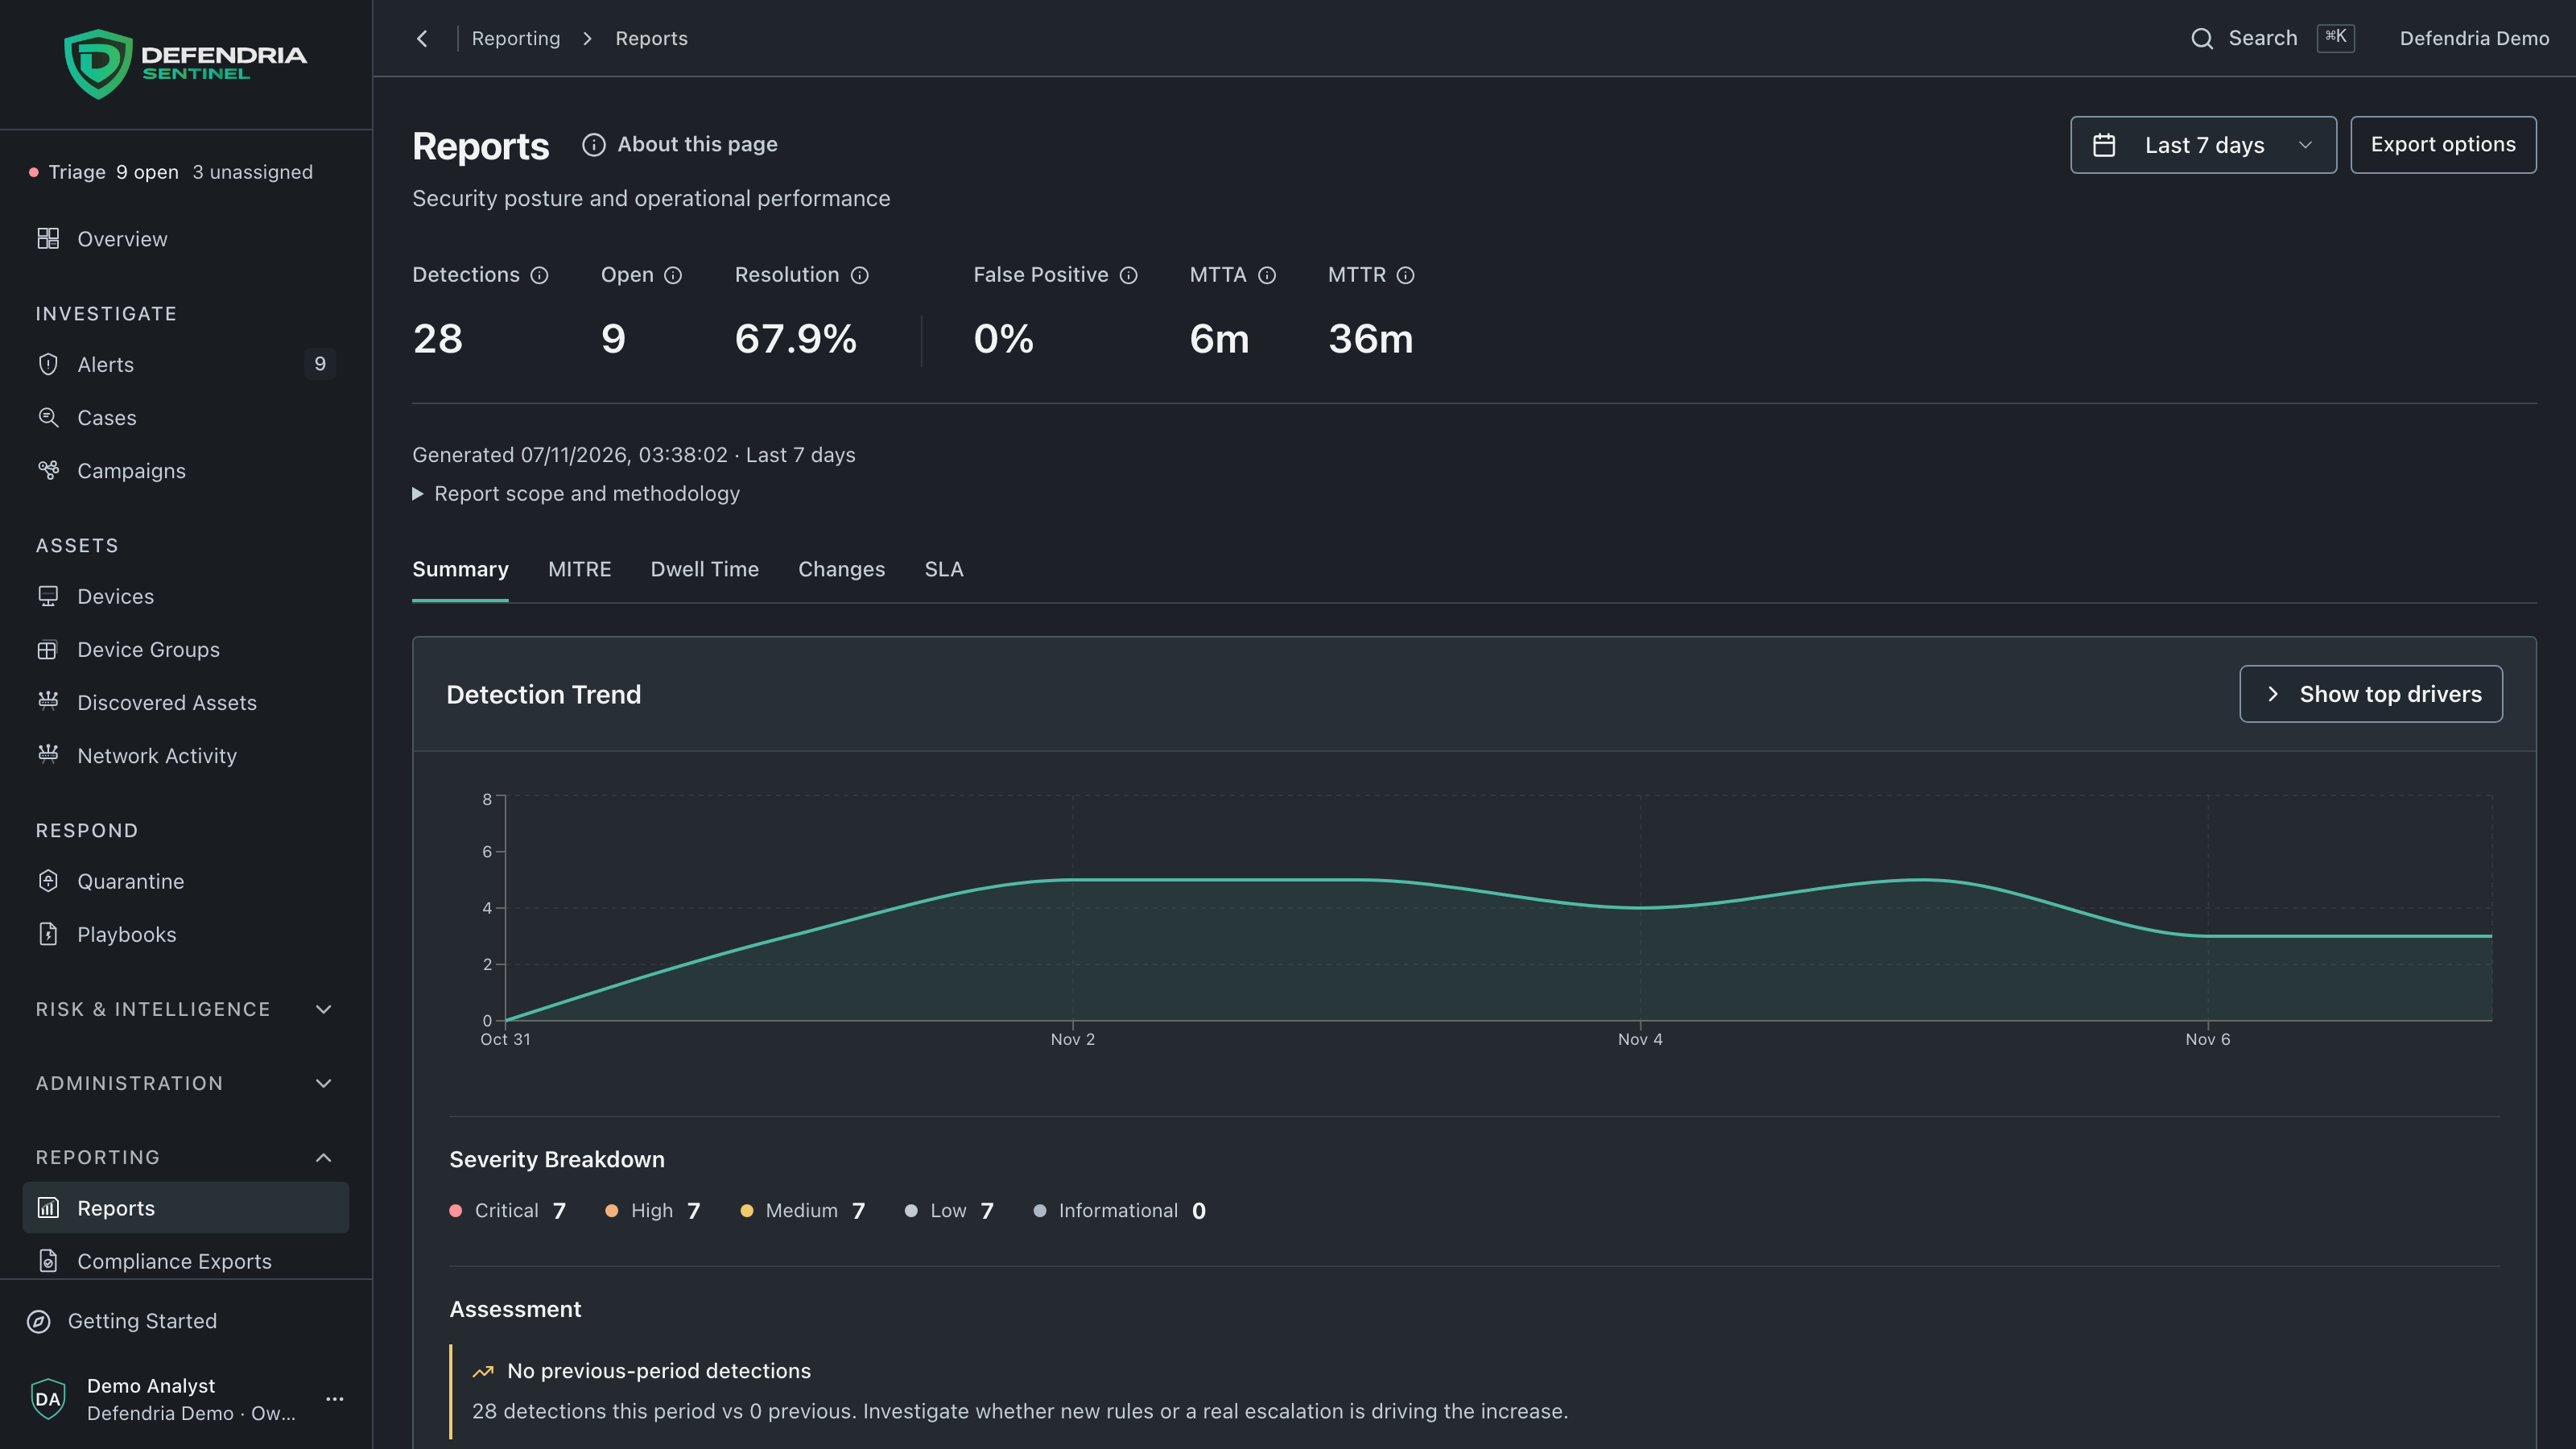
Use detection trends, severity breakdowns and response-time reports for team and management reviews.
Sentinel threat coverage
Review credential access, redirected traffic and exploitation signals.
Working as a team
Keep assignment, status and related alerts together so colleagues can see who is handling the investigation.
Give the next person the case history and supporting evidence when they pick up the work.
Check response status and action history. A request is distinct from its reported result.
Cross-device correlation
Find devices and incidents linked by a shared hash, source IP or process activity. Review each link before drawing conclusions.
Threat intelligence
Look up indicators in workspace intelligence and connected reputation services, then return to the original finding.
Threat-intelligence access depends on your plan and the reputation services connected to Sentinel.
Review Defendria’s data handling, processing terms and support commitments before choosing a provider.
Explore security & trustSecurity disclosuressecurity@defendria.com
Privacy questionsprivacy@defendria.com
Product supportsupport@defendria.com
Start with a walkthrough, review licensing and prepare a rollout that fits your environment.
Deployment & evaluationBook a guided console walkthrough before installing an agent.
Book a demoCompare per-endpoint plans, billing options and included capabilities.
Pricing & licensingUse the practical guides for enrollment, reporting, policies and everyday tasks.
Documentation & helpTell us how you manage endpoints and where security work gets stuck. We’ll focus the demo on those tasks.
Request a demo